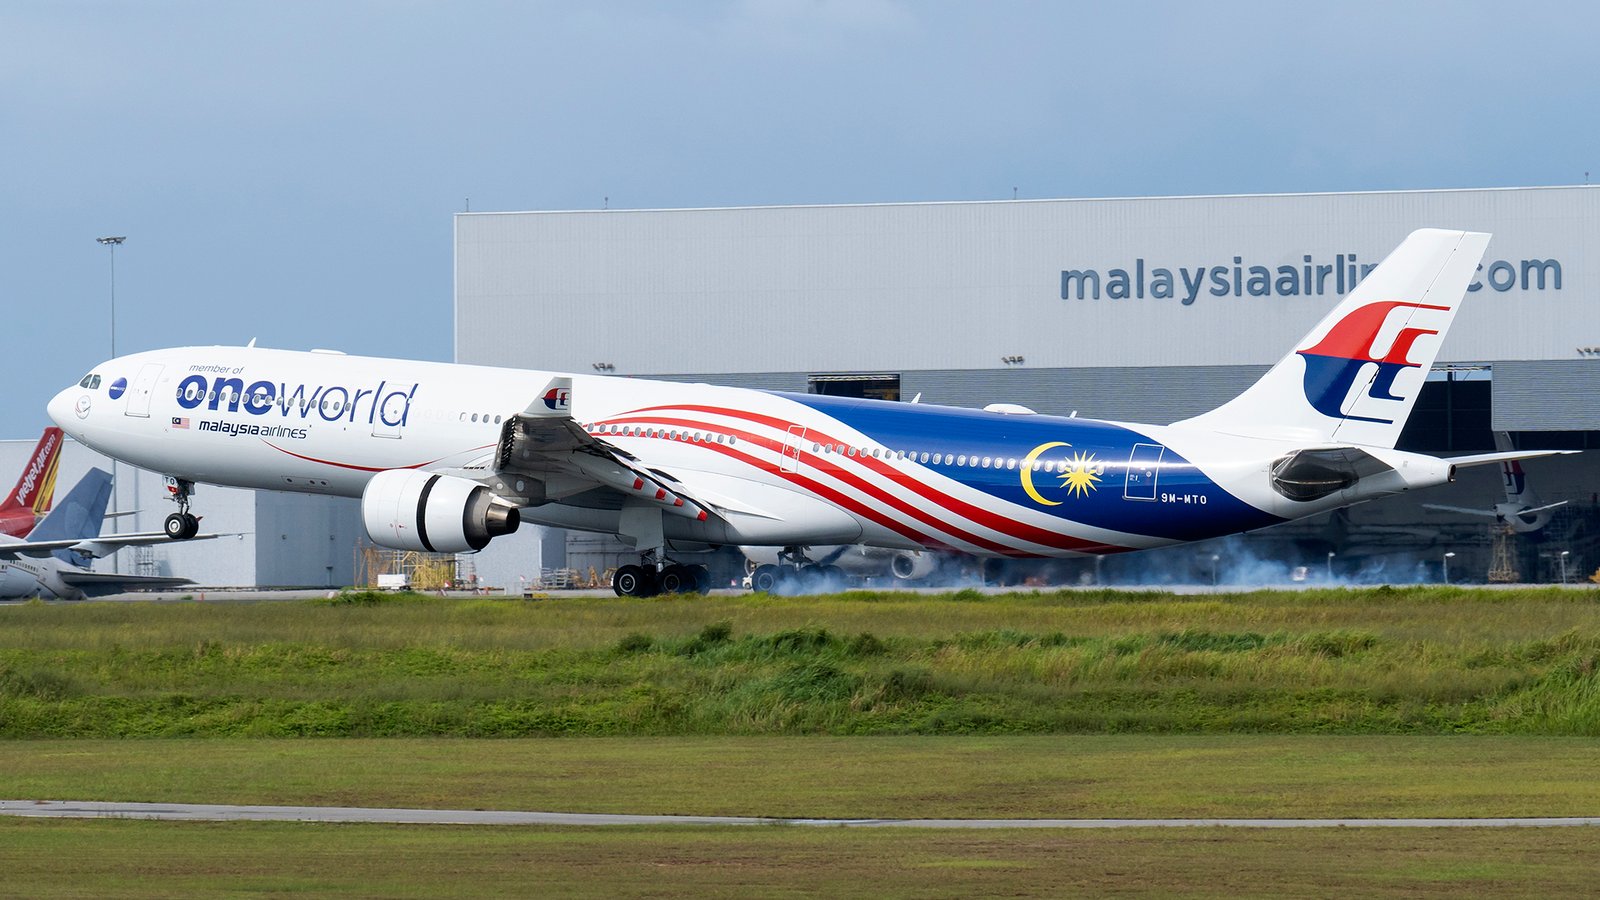
Malaysia Airlines has become the latest carrier to say its customers may have been caught up in a cybersecurity incident involving Amadeus, the travel-technology company whose systems handle bookings for airlines around the world.
The Malaysian flag carrier said on Sunday that information processed between August 2023 and September this year may have been affected. It said it was working with Amadeus and other relevant parties to investigate the incident and assess its impact.
Malaysia Airlines stressed that its own IT systems were not breached, and said there was no evidence that financial information had been accessed. It urged customers to stay alert for suspicious or unsolicited messages, particularly any asking for personal or financial details.
The disclosure widens a breach that has already prompted warnings from several carriers in Asia in recent days. Cathay Pacific has reported about 53,000 bookings affected, while Japan Airlines and Japan Transocean Air have reported about 92,000 customers affected, and All Nippon Airways about 37,800. Asiana Airlines and Korean Air have also reported customer data being compromised through Amadeus, according to Reuters.
For most of the affected records reported by other carriers, the information involved was a passenger name, a booking reference and flight details. A smaller number of records at some airlines may also have included email addresses, telephone numbers, travel-document details or frequent-flyer numbers. Malaysia Airlines has not, in the statement reported by Reuters, specified which fields were involved in its case, and that detail should be treated as still unconfirmed for Malaysia Airlines specifically.
Cathay Pacific has said Amadeus told it that an unauthorised party used login credentials assigned to a system account to reach reservation data. Amadeus itself has described a vulnerability affecting a travel booking display environment, but has not answered questions about how many customers in total were affected. That gap matters: because Amadeus sits behind so many airlines’ reservations, a single weakness in its systems can ripple across carriers that never suffered a breach of their own networks.
The incident underlines a familiar risk in modern travel. Booking details alone — a real name, a real booking reference and a real flight — can make a phishing message far more convincing than a generic scam. Airlines have therefore focused their advice on vigilance rather than on flight disruption, and none of the carriers reporting so far has said its operations were affected.
Investigations are continuing, and further carriers may yet come forward as Amadeus and its airline customers work through which records were exposed. Until a fuller account is published, passengers who booked through the affected carriers should treat unexpected messages quoting their travel details with particular caution.
Sources: Reuters, “Malaysia Airlines says customers may be affected by Amadeus breach”, 1 November 2026, https://www.reuters.com/legal/litigation/malaysia-airlines-says-customers-may-be-affected-by-amadeus-breach-2026-11-01/