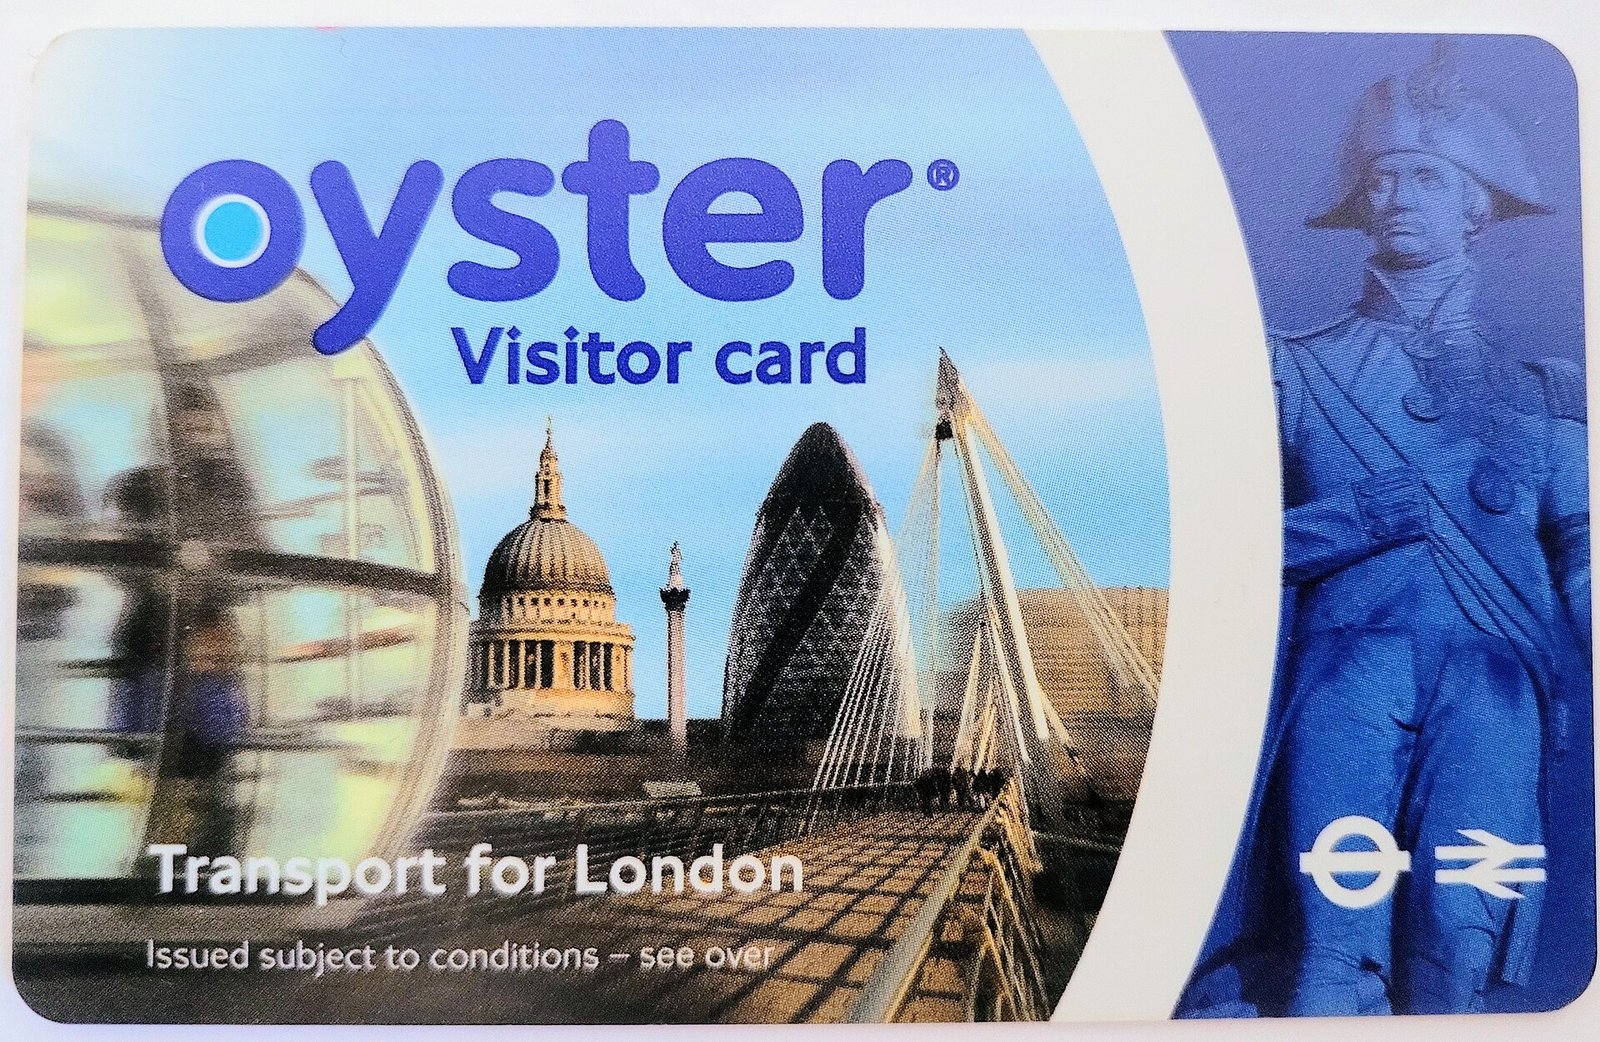
Transport for London has taken its Oyster photocard website offline after a security breach that may have compromised the account details of around 265,000 customers.
The transport authority said it became aware of the problem on Monday 16 November, when Oyster photocard customers began receiving emails asking them to create an account they already held. The emails came from TfL’s own systems, but were generated as a result of the compromise.
“We immediately took the TfL photocard website down while this was being investigated,” said Shashi Verma, TfL’s director of technology strategy and revenue. “While we acted swiftly, we now believe that around 265,000 photocard customers may have had their account details compromised as part of this incident.”
TfL said it has contained the incident, contacted the customers affected and notified the Information Commissioner’s Office. It has found no evidence so far that the compromised data has been used, and its investigation is continuing.
The accounts potentially affected cover Zip Oyster cards for children and young people aged 5 to 18, as well as 18+ Student, 18–25 Care Leaver, 60+ London, Apprentice and Veterans Oyster photocards.
According to a customer notification shared online, the information accessed may have included names, email addresses, phone numbers, home addresses, dates of birth and account security questions and answers. That detail has not been confirmed in TfL’s public statements, so it should be treated as single-sourced for now.
TfL’s current assessment is that no passwords, bank or payment card details, or customer journey information were compromised, and that the names and dates of birth of children holding Zip Oyster cards were not accessed. The authority has not yet said how the unauthorised access happened, and the estimate of 265,000 affected customers may rise as the investigation continues.
Existing photocards remain valid for travel, and holders can still use them at ticket barriers as normal. Customers who need to renew a card or check their journey history will have to contact TfL’s customer services team while the website is out of action, and there is no word yet on when it will return. Holders of 60+ photocards due an annual address check have been asked to revisit the site from 23 November.
The incident is the second major cyber breach to hit TfL in just over two years. A cyberattack in September 2024 also exposed customer data, and led to weeks of disruption to some of the authority’s online services.
Sources: The Register (https://www.theregister.com/security/2026/11/19/tfl-takes-oyster-photocard-website-offline-after-attackers-compromise-customer-accounts/5310985), BleepingComputer (https://www.bleepingcomputer.com/news/security/transport-for-london-breach-exposes-265-000-oyster-card-users-data/), Press Association via the Clacton and Frinton Gazette (https://www.clactonandfrintongazette.co.uk/news/26742936.essex-oyster-users-warned-major-tfl-data-breach/)